


The clients at home and abroad strive to buy our 312-50v13 test materials because they think our products are the best study materials which are designed for preparing the test ECCouncil certification. They trust our 312-50v13 certification guide deeply not only because the high quality and passing rate of our Certified Ethical Hacker Exam (CEH v13 AI) qualification test guide but also because our considerate service system. They treat our 312-50v13 study materials as the magic weapon to get the ECCouncil certificate and the meritorious statesman to increase their wages and be promoted. You may be not quite familiar with our 312-50v13 test materials and we provide the detailed explanation of our 312-50v13 certification guide as follow for you have an understanding before you decide to buy.
Simple language
The language of our Certified Ethical Hacker Exam (CEH v13 AI) qualification test guide is simple. The learners may come from many social positions and their abilities to master our 312-50v13 test materials are varied. Based on this consideration we apply the most simple and easy-to-be-understood language to help the learners no matter he or she is the students or the in-service staff, the novice or the experienced employee which have worked for many years. 312-50v13 certification guide use the simple language to explain the answers and detailed knowledge points and the concise words to show the complicated information about the 312-50v13 test materials. The language is also refined to simplify the large amount of information. So the learners have no obstacles to learn our 312-50v13 certification guide.
Any electronic equipment available on the APP online version
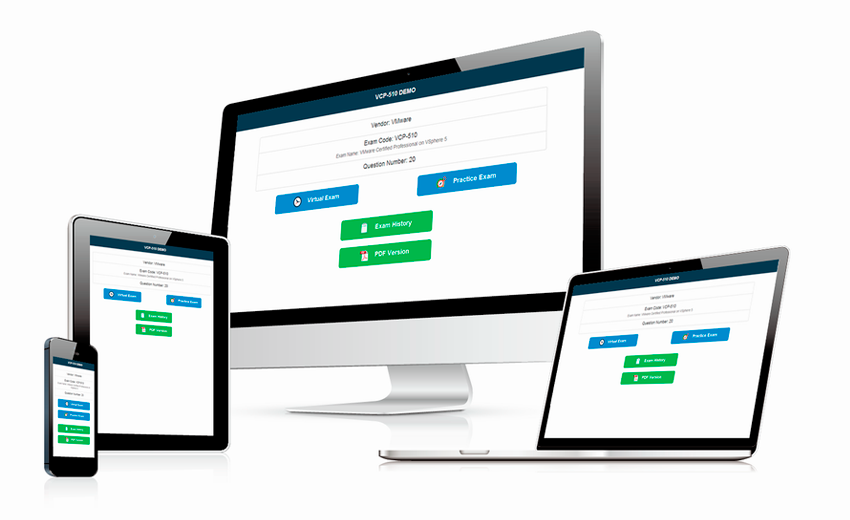
Our 312-50v13 test materials boost three versions and they include the PDF version, PC version and the APP online version. The clients can use any electronic equipment on it. If only the users' equipment can link with the internet they can use their equipment to learn our Certified Ethical Hacker Exam (CEH v13 AI) qualification test guide. They can use their cellphones, laptops and tablet computers to learn our 312-50v13 study materials. The great advantage of the APP online version is if only the clients use our 312-50v13 certification guide in the environment with the internet for the first time on any electronic equipment they can use our 312-50v13 test materials offline later. So the clients can carry about their electronic equipment available on their hands and when they want to use them to learn our Certified Ethical Hacker Exam (CEH v13 AI) qualification test guide they can take them out at any time and learn offline. So the clients can break through the limits of the time, equipment, place and environment and learn our 312-50v13 certification guide at their own wills. This is an outstanding merit of the APP online version.
Self-learning and self-evaluation functions
Our Certified Ethical Hacker Exam (CEH v13 AI) qualification test guide boosts the self-learning and self-evaluation functions so as to let the clients understand their learning results and learning process, then find the weak links to improve them. Through the self-learning function the learners can choose the learning methods by themselves and choose the contents which they think are important. Through the self-evaluation function the learners can evaluate their mastery degree of our 312-50v13 test materials and their learning process. The two functions can help the learners adjust their learning arrangements and schedules to efficiently prepare the exam. The clients can record their self-learning summary and results into our software and evaluate their learning process, mastery degrees and learning results in our software. According their learning conditions of our 312-50v13 certification guide they can change their learning methods and styles.
ECCouncil 312-50v13 Exam Syllabus Topics:
| Section | Objectives |
|---|---|
| Cloud and IoT Security | - Cloud computing security concepts - IoT security fundamentals |
| Reconnaissance Techniques | - Scanning networks and enumeration - Footprinting and information gathering |
| System Hacking | - Malware threats and system exploitation - Gaining access and privilege escalation |
| Cryptography | - Encryption, hashing, and cryptanalysis |
| Introduction to Ethical Hacking | - Ethical hacking concepts and methodology |
| Wireless and Mobile Security | - Mobile platform vulnerabilities - Wireless network attacks |
| Network Attacks | - Denial of Service (DoS/DDoS) - Sniffing and session hijacking |
| Web and Application Security | - Web application hacking techniques |
ECCouncil Certified Ethical Hacker Exam (CEH v13 AI) Sample Questions:
During a cloud security assessment, it was discovered that a former employee still had access to critical resources months after leaving the organization. Which practice would have most effectively prevented this issue?
- A. Implementing real-time traffic analysis
- B. Conducting regular penetration tests
- C. Using multi-cloud deployment models
- D. Enforcing timely user de-provisioning
Correct Answer: D 🗳️
Explanation: Only visible for LatestCram members. You can sign-up / login (it's free).
A technology startup in San Jose, California, hosts multiple customer-facing applications behind a shared Nginx reverse proxy that distributes requests to different backend services.
During an authorized security assessment, an ethical hacker analyzes how the proxy routes incoming requests to internal application servers. While experimenting with crafted HTTP requests, the tester modifies certain header values before they reach the proxy. Under specific conditions, the proxy routes the request to an unexpected backend destination rather than the legitimate internal service.
Further analysis shows that the manipulated header causes the reverse proxy to alter its routing behavior, resulting in the client receiving content served from an attacker-controlled server instead of the intended backend application.
Identify the web server attack technique demonstrated in this scenario.
- A. Frontjacking Attack
- B. Web Cache Poisoning Attack
- C. HTTP Response-Splitting Attack
- D. Directory Traversal Attack
Correct Answer: A 🗳️
Explanation: Only visible for LatestCram members. You can sign-up / login (it's free).
Why is using Google Hacking justified during passive footprinting?
- A. Mapping internal network structures
- B. Discovering hidden organizational data indexed by search engines
- C. Locating phishing sites mimicking the organization
- D. Identifying weaknesses in website source code
Correct Answer: B 🗳️
Explanation: Only visible for LatestCram members. You can sign-up / login (it's free).
While simulating a reconnaissance phase against a cloud-hosted retail application, your team attempts to gather DNS records to map the infrastructure. You avoid brute-forcing subdomains and instead aim to collect specific details such as the domain's mail server, authoritative name servers, and potential administrative information such as serial number and refresh interval.
Given these goals, which DNS record type should you query to extract both administrative and technical metadata about the target zone?
- A. MX
- B. SOA
- C. NS
- D. TXT
Correct Answer: B 🗳️
Explanation: Only visible for LatestCram members. You can sign-up / login (it's free).
In Miami, Florida, a luxury resort deploys smart climate control units in guest rooms. During a red team engagement, ethical hacker Sophia Bennett discovers that once a compromised device is restarted, it continues running altered instructions without any integrity check before the operating system loads. This allows tampered firmware to run as if it were legitimate. Which secure development practice would most directly prevent this weakness?
- A. Allow code signing
- B. Ensure secure boot
- C. Utilize secure communication protocols
- D. Secure firmware or software updates
Correct Answer: B 🗳️
Explanation: Only visible for LatestCram members. You can sign-up / login (it's free).


 Hardy

 Judith

 Mandel
 Liz

 Derrick
 Dean
 Meredith
 Abigail
 Jonas
 Edmund
 Kimberley
 Abigail
 Karen
 Theresa
 Jerry


